

SOC architectures are usually designed as a pipeline. Logs go into a SIEM, correlation rules turn them into alerts, and each alert moves to an analyst before anything else happens. Every stage waits on the one before it, and the analyst sits in the middle of all of them.
An AI SOC architecture is built in layers instead. Each layer passes structured output to the next: telemetry feeds a data lake, the data lake feeds detection models, detection drives automated response, and analyst decisions flow back into the models. Below, we go through the six layers one by one, what each needs to work, and how they fit on top of an existing SIEM and SOAR.
What Is an AI-Driven SOC?
An AI-driven security operations center (SOC) uses machine learning, behavioral analytics, and automation to detect, enrich, and contain threats, while analysts focus on investigation and judgment. Telemetry from endpoints, cloud, identity, and the network flows into a security data lake. AI models score risk across every user and asset. SOAR playbooks contain high-confidence threats in seconds. Every analyst decision feeds back into the models, so the system improves with use. A traditional SOC relies on rules that fire alerts for analysts to work through one at a time. An AI-driven SOC scores, correlates, and acts on signals in parallel, and escalates only what needs human judgment. For a side-by-side view, see how traditional and AI-powered SOCs compare.
The Six Layers of an AI SOC Architecture
An AI SOC architecture is a modern SOC architecture built in six interconnected layers. Each handles a distinct function in the detection and response lifecycle, and each produces structured output that feeds the next:
- Layer 01, Telemetry: Collects events from endpoints, network, cloud, identity, and SaaS applications.
- Layer 02, Security data lake: Stores raw events at full fidelity and normalizes them at query time.
- Layer 03, AI detection engine: Scores risk through anomaly detection, UEBA, threat intelligence, and LLM-assisted triage.
- Layer 04, Automated response: Runs SOAR playbooks and AI-led investigation when confidence crosses a defined threshold.
- Layer 05, Human analyst tier: Handles threat hunting, complex incidents, and decisions with business or legal consequences.
- Layer 06, Continuous learning loop: Turns every analyst decision into training data for the models.
The architectural premise is simple: automate high-volume, low-ambiguity work at machine speed, and concentrate analyst attention on decisions that need human judgment.
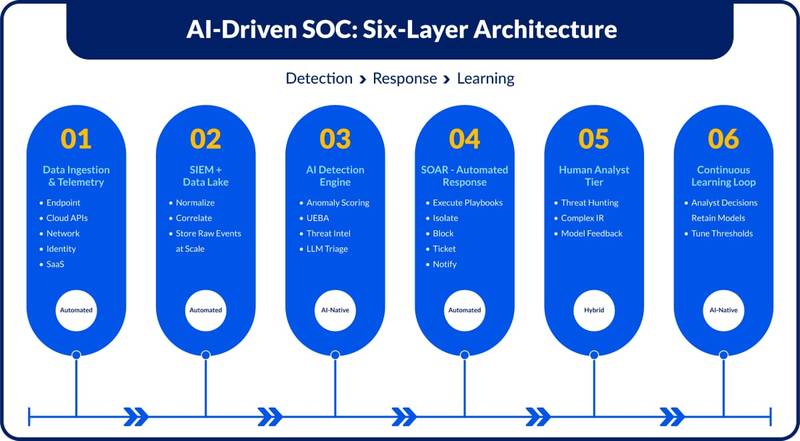
Detection and containment can complete a full automated cycle before an analyst receives a notification. The human tier handles ambiguous investigations, novel threat patterns, and decisions with business or legal consequences.
Layer 01–02: Telemetry Coverage Across the Attack Surface
Every downstream AI capability is bounded by the quality and completeness of the data it receives. Telemetry coverage is the most foundational architectural decision in SOC modernization and the most frequently under invested one. A mature AI-native SOC ingests across the full attack surface:
- EDR agents on every managed endpoint
- Firewall, proxy, and DNS logs
- Cloud provider API trails – AWS CloudTrail, Azure Activity Log, GCP Audit
- Identity and access events: Okta, Microsoft Entra ID, CyberArk
- SaaS application logs via CASB connectors
- Deception assets – honeypots and canary tokens for high-fidelity early warning
Layer 02: The Security Data Lake
The security data lake is where telemetry becomes usable. It stores full-fidelity events from every source and keeps them queryable for detection, investigation, and retrospective hunting. The way in which it handles schema decides how quickly new sources can be added. Teams moving off a legacy SIEM usually start here.
Schema-on-read vs. schema-on-write
Legacy SIEMs enforced schema at write time. Every source had to be normalized into a fixed format before storage. That created:
- Data loss for any fields outside the predefined schema
- Slow, painful onboarding whenever a new log source was added
- Brittle pipelines that broke when vendors changed log formats
Modern data lakes, such as Google Security Operations (formerly Chronicle), Microsoft Sentinel, and Elastic Security, ingest raw events and normalize at query time instead. The Open Cybersecurity Schema Framework (OCSF) provides a vendor-neutral taxonomy that makes cross-source normalization consistent. Query-time normalization enables:
- Faster source onboarding
- Full-fidelity event retention
- Ability to run retrospective queries when new detection logic is developed.
Establish formal telemetry coverage targets before deploying ML detection. Model sophistication cannot compensate for gaps in visibility. We recommend 100% telemetry coverage of crown-jewel assets as the minimum floor.
Layer 03: The AI Detection Engine
The detection engine runs four capabilities in parallel, each targeting a different threat class. The combined output is a continuous, enriched risk picture across every user, host, and application in the environment. Analysts work from ranked risk, which is how an AI SOC reduces alert fatigue.
Statistical anomaly detection
Statistical models are built on per-entity baselines across users, hosts, applications, and network endpoints. Each deviation produces a risk score that feeds a broader risk aggregation model. A single deviation rarely triggers an alert on its own. Detection signals include:
- Impossible travel – authentication from two distant locations within minutes
- Unusual outbound ports on a server that has never used them
- Processes spawning unexpected child trees
Common implementations use time-series analysis for volume anomalies, isolation forests for behavioral outliers, and k-means clustering for peer group deviations. The key design choice is output format: a continuous score that aggregates with other signals produces far fewer spurious alerts than a binary threshold.
User and Entity Behavior Analytics
Where anomaly detection flags individual data points, UEBA identifies patterns that only become significant in sequence. An after-hours login is a low signal. The same login followed by bulk file enumeration, an archive operation, and an upload to an external domain is a high-confidence exfiltration pattern – even if no individual event crossed a threshold. Implementation notes:
- Typically built on RNNs or transformer architectures, learning temporal patterns across long lookback windows
- Needs several months of baseline telemetry before producing reliable output; the exact period depends on the size and variability of the environment
- Deployments that skip the baseline period see high false positive rates early, eroding analyst trust before the feedback loop has a chance to stabilize.
Threat intelligence enrichment
Alongside behavioral analysis, every observable extracted from events, including IPs, domains, file hashes, and certificate fingerprints, is correlated against threat feeds in near real time. Every alert arrives with its threat intelligence context attached.
| Commercial feeds | Recorded Future, CrowdStrike Falcon Intelligence |
|---|---|
| Open-source | VirusTotal, AlienVault OTX, MISP instances |
| Sector-specific | ISACs (Information Sharing and Analysis Centers) |
| Lookup method | In-memory for high-frequency; async API for lower-frequency observables |
By the time an alert surfaces to an analyst, its indicators have already been cross-referenced. Lookups that analysts once ran by hand for every alert now happen automatically. The analyst opens a case that has already been investigated at the IOC level.
LLM-assisted triage
The LLM layer sits downstream of detection and enrichment. When an incident fires, the model assembles a full context with raw events, UEBA scores, IOC findings, asset ownership from CMDB, recent user access history, and produces a structured summary covering: What occurred and the event sequence
- What occurred: The event sequence, in order.
- Why it is suspicious: What the risk score reflects.
- Likely objective: What the attacker appears to be trying to achieve.
- ATT&CK mapping: The MITRE ATT&CK techniques implicated.
LLM-generated summaries also create a consistent, auditable record of why each alert was actioned. That record supports the incident documentation behind SEC cybersecurity disclosure obligations in the US, and NIS2 and DORA incident reporting in the EU.
MITRE ATT&CK coverage
| Tactic | Technique | AI Detection Signal |
|---|---|---|
| Initial Access | Spearphishing link (T1566.002) | Email anomaly + click on unusual domain |
| Privilege Escalation | Valid accounts (T1078) | UEBA: atypical access time and scope |
| Lateral Movement | Pass-the-hash (T1550.002) | Same credentials reused across multiple hosts in rapid succession |
| Exfiltration | Exfiltration over web service (T1567) | Volume anomaly + threat intel hit on destination domain |
| Impact | Data encrypted (T1486) | Mass file extension changes + shadow copy deletion |
The detection engine’s output is a continuously updated risk picture across every entity in the environment, ranked by what needs attention first.
Layer 04: Automated Response and AI Agents
Security orchestration, automation, and response (SOAR) automates repetitive security tasks such as alert enrichment, ticket creation, account suspension, and endpoint isolation. It executes structured playbooks when detection confidence crosses a defined threshold. That threshold is risk-calibrated.
| Low-impact actions (lower confidence threshold) | Alert enrichment, ticket creation, asset owner notification – auto-executed |
|---|---|
| High-impact actions (higher threshold or approval) | Endpoint isolation, account suspension, firewall rule insertion – requires higher confidence or explicit analyst sign-off |
Integration depth determines value
The SOAR layer’s value is proportional to how deeply it integrates with the toolstack. Shallow integrations that only create tickets return marginal value. Deep, bidirectional integrations with EDR platforms, identity providers, firewall APIs, and CMDB systems are what enable the containment speed that defines an AI-native SOC.
Agentic Investigation: How AI Agents Work in the SOC
An AI agent in the SOC investigates an alert the way an analyst would. It decides which data to query, gathers identity, endpoint, and network context, tests a hypothesis, and drafts a verdict with its evidence. SOAR playbooks follow fixed steps; agents plan the steps. The analyst reviews the reasoning and approves or redirects it.
- Query planning: The agent chooses which logs and tools to check for this specific alert.
- Context gathering: It pulls asset ownership, user history, and related alerts through existing integrations.
- Evidence-backed verdicts: Each conclusion links to the events that support it.
- Bounded actions: Agents act only through approved tools and permissions, and every step is logged.
Agents widen what automation can cover. They also widen what governance must control, including scoped permissions, logged actions, and approval for high-impact steps.
Response lifecycle
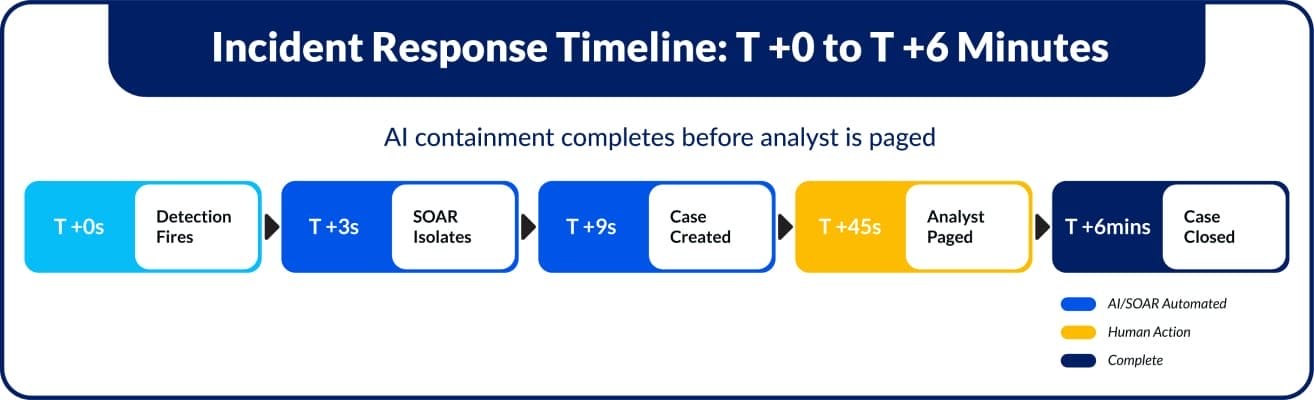
For example, if a high-confidence lateral movement detection fires, the automated response lifecycle could run like this:
T + 0s
Detection fires at 94% confidence Lateral movement: credential reuse across 3 hosts in 90 seconds, unusual process spawning on a domain controller.
T + 3s
SOAR executes containment playbook Endpoint isolated via EDR. User account suspended in Okta. Active sessions revoked. Firewall rule blocks the source IP.
T + 9s
Enrichment and case creation Asset owner pulled from CMDB. IOCs checked against threat feeds. LLM generates an incident summary. Ticket created in ServiceNow.
T + 45s
On-call analyst paged Incident already contained. Analyst role: confirm response, identify initial access vector, assess blast radius.
T + 6min
Case closed with analyst feedback Confirmed true positive. Access path documented. Correlated alerts marked – signals enter training pipelines. In this example, detection, isolation, enrichment, and documentation complete in under 10 seconds. The analyst’s first action is review and confirmation. Automated containment actions carry business risk. A playbook that incorrectly isolates a production server causes operational disruption. Approval workflows, impact classifications, and quarterly playbook reviews are operational necessities.
AI-Assisted vs. Autonomous Response
How much should the AI decide on its own? Most enterprises use a tiered model and move actions between tiers as trust builds:
- AI-assisted: AI enriches, summarizes, and recommends. Analysts take every action.
- Supervised autonomy: AI executes low-impact actions automatically and proposes high-impact ones for analyst approval.
- Autonomous: AI runs defined playbooks end to end within a strict scope, and analysts review after the fact.
Autonomy should expand one action type at a time, as the learning loop shows that the model’s decisions hold up in your environment. Isolating a laptop and isolating a production server belong at very different tiers.
Layer 05: The Human Analyst Tier
In a well-calibrated AI SOC, the human tier handles what automation can’t. Some decisions require contextual judgment, adversarial intuition, and accountability that no current system provides. Tier 1 triage largely disappears as a primary function. That capacity shifts to:
- Threat hunting – proactively querying the data lake for undetected compromise
- Complex incident response – multi-stage attacks, supply chain intrusions, nation-state activity
- Detection engineering – improving model coverage based on emerging TTP intelligence
- Risk communication – translating technical findings into business-risk language for leadership
Performance Shift: Traditional SOC vs AI-Native SOC
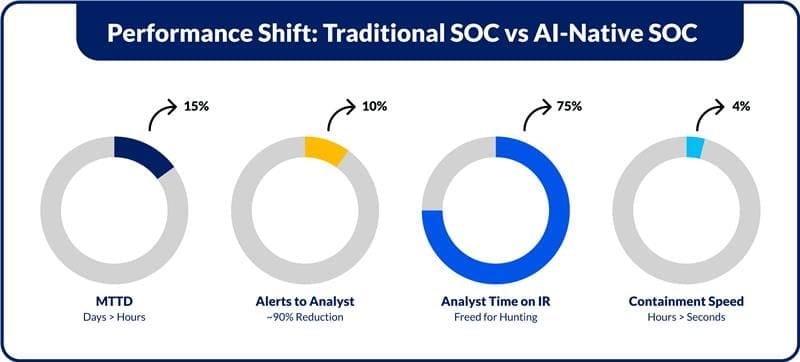
Threat hunting at depth
With triage handled automatically, analyst time opens up for proactive hunting. This includes:
- Living-off-the-land techniques that blend with normal administrative behavior
- Novel malware families without known signatures
- Attacker dwell patterns that fall just below anomaly detection thresholds
This work requires deep knowledge of attacker TTPs and OS internals. It is not something the current generation of AI models replicates.
Complex incident response
Multi-stage attacks and nation-state intrusions require human-directed investigation. The AI layer compresses time to context: the analyst arrives with enriched data, correlated events, and an LLM-generated summary already assembled, so incident response starts with the evidence already in hand. What remains human:
- Forensic reasoning
- Acquisition sequencing
- Interpretation of ambiguous artefacts
- Escalation decisions
- Communication to legal and executive stakeholders
Layer 06: The Continuous Learning Loop
The feedback loop is what separates a static automation platform from a system that improves over time. Every analyst’s decision generates a labeled data point that feeds back into model retraining:
- Confirmed true positive – weights that event sequence more heavily in future scoring
- False positive correction – teaches the model to discount that signal combination in this environment
- Investigation notes – improve LLM summary quality for similar future case types
The feedback loop is the mechanism through which the system earns the right to operate with more autonomy over time.
What an AI-Powered SOC Stack Looks Like
Most enterprises already own several of these components. The architecture question is how they connect: which signals each layer passes to the next, and where decisions are automated.
- Telemetry: EDR agents, firewall, proxy, and DNS logs, cloud audit trails, identity provider events, CASB connectors, and deception assets.
- Security data lake: A SIEM or security analytics platform such as Splunk, Microsoft Sentinel, Google Security Operations, or Elastic Security, with OCSF-based normalization.
- Detection: UEBA, ML anomaly models, threat intelligence feeds, and an LLM layer for triage summaries.
- Response: A SOAR platform integrated with EDR, the identity provider, firewall APIs, the CMDB, and ITSM tools such as ServiceNow.
- Analyst tier: Case management, a hunting workspace on the data lake, and detection-as-code tooling.
- Learning loop: Labeled case outcomes, model retraining pipelines, and scheduled evaluation against labeled datasets.
For how these layers come together on a Splunk-based stack, see how Splunk powers the AI SOC.
How to Build an AI-Powered SOC on an Existing Stack
To build an AI-powered SOC on an existing SIEM, SOAR, and EDR stack, work through the layers in order: telemetry coverage, data foundation, behavioral baselines, low-impact automation, then the feedback loop. Each layer depends on the one before it:
- Start with telemetry coverage: Set coverage targets for crown-jewel assets and close gaps in identity and cloud logs first.
- Fix the data foundation: Move to query-time normalization and retain full-fidelity events, so models and hunts have history to work from.
- Baseline before you detect: Run UEBA in observation mode until behavioral baselines stabilize, before its scores drive alerts.
- Automate low-impact actions first: Start SOAR with enrichment and ticketing, then add containment as confidence and integrations mature.
- Wire the feedback loop from day one: Capture analyst verdicts as labeled data, even before retraining pipelines are in place.
Three requirements apply at every step: deep, bidirectional integrations with existing tools; analysts trained to review and correct AI decisions; and governance that defines which actions AI may take on which assets.
How to Measure AI SOC Performance
AI SOC performance is measured with six operational metrics: MTTD, MTTR, attacker dwell time, false positive rate, share of alerts closed automatically, and analyst time on hunting and engineering. Baseline each one before making changes, then track which layer moves it:
- Mean time to detect (MTTD): Reflects telemetry coverage and detection quality.
- Mean time to respond (MTTR): Reflects SOAR integration depth and playbook coverage.
- Attacker dwell time: Reflects detection and hunting working together.
- False positive rate: Reflects UEBA baselines, enrichment, and the health of the feedback loop.
- Share of alerts closed automatically: Shows how much low-ambiguity work automation absorbs.
- Analyst time on hunting and engineering: Shows whether capacity actually shifts away from triage.
Compare each metric with your own baseline over a matching time period. Vendor benchmarks rarely reflect your environment.
Architectural Risks and Governance Controls
Each layer introduces specific risks when misconfigured or underinvested. Addressing them at the architecture level is structurally more effective than responding reactively.
| Telemetry gaps | Incomplete coverage creates a blind spot that no model compensates for. Entire threat categories can go undetected. Formal coverage targets and regular coverage audits are the controls. |
|---|---|
| UEBA without baseline | Deploying UEBA before sufficient baseline data exists floods early operation with false positives. The model has no reference point for normal. Analyst distrust follows, damaging the feedback loop before it functions. |
| Model drift | Detection models degrade silently as attacker TTPs evolve. Precision falls gradually with no visible failure event. Continuous retraining pipelines and scheduled model evaluation against labeled datasets are the controls. |
| Shallow SOAR integration | SOAR that only creates tickets returns minimal value over a well-configured SIEM. Containment speed depends on deep integrations with EDR, IdP, and network control planes. Evaluate integration depth before vendor selection. |
| Ungoverned playbooks | Automated actions affecting production systems require governance. A playbook that isolates a production database without approval creates disruption. Impact classifications, approval workflows, and rollback procedures must be defined before high-impact automation goes live. |
| Ungoverned AI agents | Agents that query and act across tools need scoped permissions, logged actions, and human approval for high-impact steps. Without these, an agent error spreads at machine speed. |
| Explainability gaps | Black-box detections create compliance risk. Regulators and auditors expect organizations to explain how incidents were detected and handled, and SEC, NIS2, and DORA reporting depends on that record. |
What to Evaluate Now
Security teams are still operating on architectures designed to observe, correlate, and respond in sequence while attackers operate in parallel, at machine speed. This creates a structural gap that more tooling alone cannot close. Security architects can test their own architecture against three signals. If your SOC detects threats in minutes instead of seconds, depends on analysts to validate every decision, or cannot correlate identity, endpoint, and network signals in real time, it is already operating behind the attacker.
Each signal points to a layer: telemetry and the data lake for slow detection, response automation for analyst-bound decisions, and the detection engine for weak correlation. An AI-driven SOC is an operating model that improves continuously as long as the architecture is designed to learn, and the team is structured to let it.
Prudent works with enterprise security teams to assess telemetry coverage, data foundations, and SOAR integration depth, and to build AI-driven detection and response on platforms such as Splunk. For teams that want the outcome without building the SOC in-house, managed detection and response (MDR) delivers the same layered model as a service.
Assess Your SOC Architecture
Know where your architecture slows detection and response.